6 things worth knowing from this week
The 6 that mattered most this week, each in one line.
TCP Use-After-Free: CVE-2026-98432 / CVSS 9.8
TL;DRA critical use-after-free vulnerability in the Linux kernel IPv4 TCP handshake allows unauthenticated remote code execution.
Read on atlasum.net →pull_request_target blocked by default December 2
TL;DRGitHub Actions will block pull_request_target events by default in public repositories starting December 2, 2026.
Read on github.blog →Claude Code sends your email address to websites
TL;DRClaude Code versions 2.1.317 and later include a built-in privacy mod enabled by default to block email leakage.
Read on github.com →Postman silently auto-installs AI plugins and attempts to share all API data
TL;DRPostman 12.33.4 desktop app automatically installs Codex and Claude plugins without asking users for permission.
Read on github.com →Vitest 5: Prioritises Performance with a Shared Vite Server, Trace View, and Stricter Test Defaults
TL;DRVitest 5.0 brings 8 to 53 percent performance gains through a shared Vite server, fewer worker round trips, and optimized VM pools.
Read on infoq.com →Discord is ditching Electron and its new app uses less RAM
TL;DRDiscord is replacing Electron and React Native with Rust to power its desktop and mobile application architecture.
Read on theverge.com →Everyone's talking about
Astra can read and write weights to improve Qwen
TL;DRDemonstrates how the GPT-6 Astra model can natively read and write neural network weights without using gradient descent.
Read on rikiyat.github.io →Sshole
TL;DRDetails a vulnerability in OpenSSH affecting systems running on musl like Alpine, OpenWrt, and Yocto without PAM.
Read on sshhole.com →Your stack, every morning
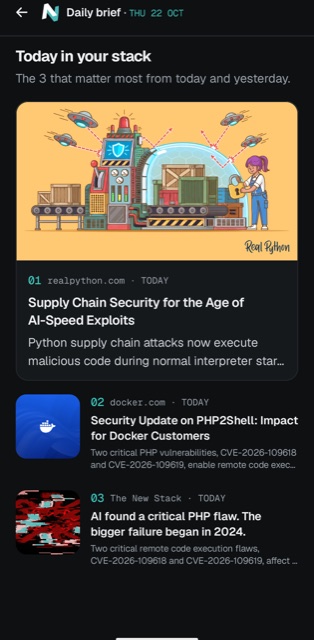
Pick your languages and tools. Code News sends a Daily brief at 9:00 and a Past week recap, with a TL;DR on every article.
Code News by CodeBldr · picked from 240+ developer sources · tap a story to read it on the original site